About Us | Insights | Careers | Industries |

Cybersecurity Risk Assessment & Consulting Services

Identify cybersecurity vulnerabilities, evaluate business risks and build a practical security improvement plan before threats disrupt your operations.

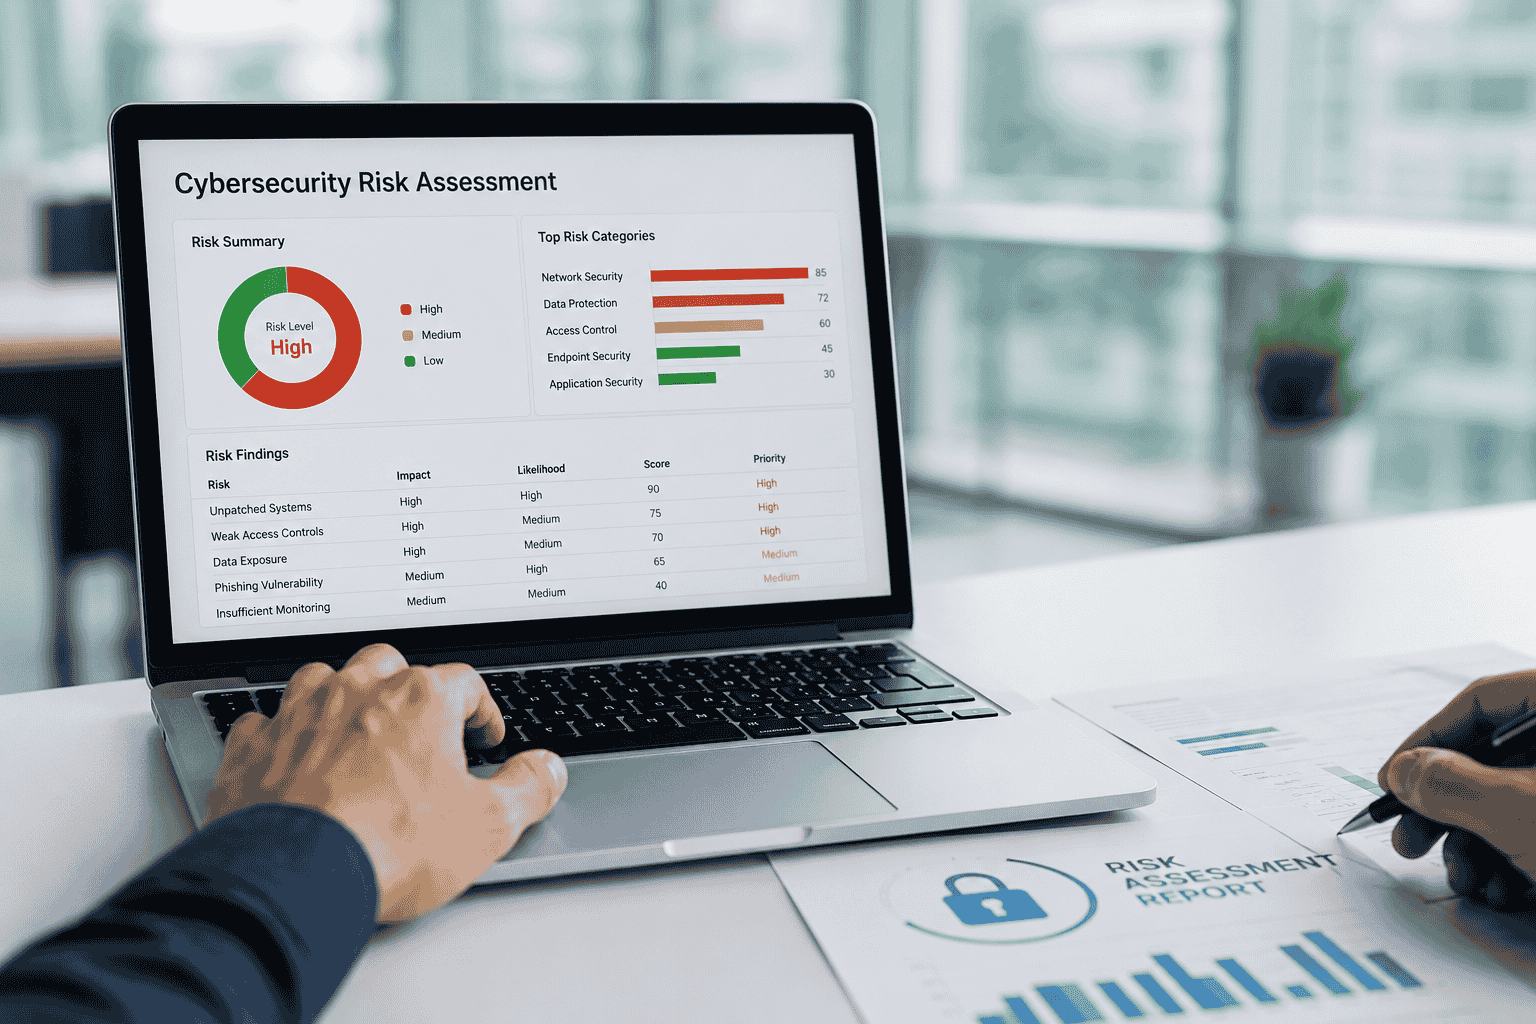
Cybersecurity risk assessment and consulting services for business IT security
Overview

Understand and Reduce Your Organisation’s Cyber Risks

Businesses depend on technology, cloud platforms, applications and digital data, but security weaknesses within these systems can expose the organisation to cyberattacks, data breaches and operational disruption.

T3 Consulting provides cybersecurity risk assessment and consulting services for businesses worldwide. We identify security vulnerabilities, evaluate cyber risks, review existing security controls and assess threats across IT infrastructure, cloud environments, applications, business processes and user access.

We translate technical findings into clear business risks and provide a prioritised cybersecurity risk management roadmap to help organisations strengthen their security posture. Our assessments also complement cloud migration services and cloud optimization services, helping businesses identify security gaps and manage risks across cloud infrastructure and digital operations.
Cyber Risk Assessment Security Gap Analysis Vulnerability Review Control Assessment Risk Reduction Roadmap
What We Assess

Comprehensive Cybersecurity Risk Assessment Services

Evaluate your cybersecurity posture across systems, users, applications, policies and third-party relationships to identify weaknesses and prioritise security improvements.

IT Infrastructure Risk Assessment

Assess servers, networks, endpoints, firewalls, cloud platforms and other critical infrastructure for security risks and control gaps.

Vulnerability and Exposure Review

Identify known vulnerabilities, insecure configurations, outdated systems and potential points of entry that attackers could exploit.

Identity and Access Risk Assessment

Review user accounts, permissions, privileged access, authentication controls and account management practices.

Data Security Assessment

Evaluate how sensitive business and customer data is collected, stored, accessed, transmitted, backed up and protected.

Policy and Security Control Review

Assess existing cybersecurity policies, procedures, governance practices and security controls against business requirements.

Third-Party and Vendor Risk Assessment

Review cybersecurity risks introduced by suppliers, service providers, cloud vendors and other external business partners.

Why It Matters

Why Businesses Need Regular Cybersecurity Risk Assessments

Cyber risks continuously change as businesses adopt new applications, cloud services, remote working practices and third-party platforms. Security controls that were effective earlier may no longer provide sufficient protection.

A cybersecurity risk assessment helps management understand where the organisation is most exposed, which risks require immediate attention and how available security budgets should be prioritised.

Identify Hidden Security Weaknesses

Discover vulnerabilities, control gaps and insecure practices before they are exploited by attackers.

Understand Business Risk

Translate technical security findings into potential financial, operational, legal and reputational impact.

Prioritise Security Improvements

Focus resources on the highest-risk systems and weaknesses instead of making unplanned security investments.

Improve Security Resilience

Strengthen preventive, detective and recovery controls to reduce the impact of potential cyber incidents.

Support Compliance and Audits

Maintain documented risk findings and remediation plans that support compliance reviews and security audits.

Cybersecurity risk management and information security risk assessment process
Our Methodology

Our Cybersecurity Risk Assessment Process

A structured assessment process to understand your technology environment, identify security risks and develop a practical improvement roadmap.

01
Scope and Information Gathering

Define the assessment scope and collect information about systems, applications, data, users, policies and business operations.

02
Risk and Control Assessment

Review vulnerabilities, threats, access controls, configurations, policies and existing cybersecurity safeguards.

03
Risk Analysis and Prioritisation

Evaluate each risk based on likelihood, potential business impact and the effectiveness of existing controls.

04
Remediation Roadmap

Deliver prioritised recommendations, practical corrective actions and a cybersecurity improvement roadmap.

Frequently Asked Questions

Cybersecurity Risk Assessment FAQs

A cybersecurity risk assessment identifies security threats, vulnerabilities and potential business risks across IT systems, applications, networks and data.

Cybersecurity consulting helps businesses identify security weaknesses, evaluate existing controls and develop practical strategies to reduce cyber risks.

An assessment may include infrastructure security, vulnerability reviews, access controls, data protection, cloud security and third-party risk evaluation.

Businesses should review cyber risks regularly and after major technology, infrastructure or operational changes.

A vulnerability assessment identifies technical weaknesses, while a cybersecurity risk assessment also evaluates threats, business impact and risk priorities.

T3 Consulting offers cybersecurity risk assessment and consulting services for businesses worldwide, helping organizations identify risks and plan security improvements.

Understand Your Cyber Risks Before Attackers Find Them

Partner with T3 Consulting to identify security weaknesses, understand business exposure and build a practical cybersecurity risk reduction plan.